
Get 100% Success with Latest Fortinet Certified Solution Specialist FCSS_SASE_AD-23 Exam Dumps Dec 01, 2024
The Best FCSS_SASE_AD-23 Exam Study Material and Preparation Test Question Dumps
NEW QUESTION # 13
Refer to the exhibit.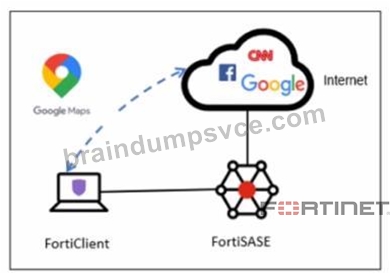
A company has a requirement to inspect all the endpoint internet traffic on FortiSASE, and exclude Google Maps traffic from the FortiSASE VPN tunnel and redirect it to the endpoint physical Interface.
Which configuration must you apply to achieve this requirement?
- A. Exempt the Google Maps FQDN from the endpoint system proxy settings.
- B. Configure a static route with the Google Maps FQDN on the endpoint to redirect traffic
- C. Change the default DNS server configuration on FortiSASE to use the endpoint system DNS.
- D. Configure the Google Maps FQDN as a split tunneling destination on the FortiSASE endpoint profile.
Answer: D
Explanation:
To meet the requirement of inspecting all endpoint internet traffic on FortiSASE while excluding Google Maps traffic from the FortiSASE VPN tunnel and redirecting it to the endpoint's physical interface, you should configure split tunneling. Split tunneling allows specific traffic to bypass the VPN tunnel and be routed directly through the endpoint's local interface.
* Split Tunneling Configuration:
* Split tunneling enables selective traffic to be routed outside the VPN tunnel.
* By configuring the Google Maps Fully Qualified Domain Name (FQDN) as a split tunneling destination, you ensure that traffic to Google Maps bypasses the VPN tunnel and uses the endpoint's local interface instead.
* Implementation Steps:
* Access the FortiSASE endpoint profile configuration.
* Add the Google Maps FQDN to the split tunneling destinations list.
* This configuration directs traffic intended for Google Maps to bypass the VPN tunnel and be routed directly through the endpoint's physical network interface.
References:
* FortiOS 7.2 Administration Guide: Provides details on split tunneling configuration.
* FortiSASE 23.2 Documentation: Explains how to set up and manage split tunneling for specific destinations.
NEW QUESTION # 14
Which FortiSASE feature ensures least-privileged user access to all applications?
- A. thin branch SASE extension
- B. SD-WAN
- C. zero trust network access (ZTNA)
- D. secure web gateway (SWG)
Answer: C
NEW QUESTION # 15
Which FortiSASE feature ensures least-privileged user access to all applications?
- A. thin branch SASE extension
- B. SD-WAN
- C. zero trust network access (ZTNA)
- D. secure web gateway (SWG)
Answer: C
Explanation:
Zero Trust Network Access (ZTNA) is the FortiSASE feature that ensures least-privileged user access to all applications. ZTNA operates on the principle of "never trust, always verify," providing secure access based on the identity of users and devices, regardless of their location.
* Zero Trust Network Access (ZTNA):
* ZTNA ensures that only authenticated and authorized users and devices can access applications.
* It applies the principle of least privilege by granting access only to the resources required by the user, minimizing the potential for unauthorized access.
* Implementation:
* ZTNA continuously verifies user and device trustworthiness and enforces granular access control policies.
* This approach enhances security by reducing the attack surface and limiting lateral movement within the network.
References:
* FortiOS 7.2 Administration Guide: Provides detailed information on ZTNA and its role in ensuring least-privileged access.
* FortiSASE 23.2 Documentation: Explains the implementation and benefits of ZTNA within the FortiSASE environment.
NEW QUESTION # 16
Which two deployment methods are used to connect a FortiExtender as a FortiSASE LAN extension? (Choose two.)
- A. Configure an IPsec tunnel on FortiSASE to connect to FortiExtender.
- B. Enter the FortiSASE domain name in the FortiExtender GUI as a static discovery server
- C. Connect FortiExtender to FortiSASE using FortiZTP
- D. Enable Control and Provisioning Wireless Access Points (CAPWAP) access on the FortiSASE portal.
Answer: B,C
Explanation:
There are two deployment methods used to connect a FortiExtender as a FortiSASE LAN extension:
* Connect FortiExtender to FortiSASE using FortiZTP:
* FortiZero Touch Provisioning (FortiZTP) simplifies the deployment process by allowing FortiExtender to automatically connect and configure itself with FortiSASE.
* This method requires minimal manual configuration, making it efficient for large-scale deployments.
* Enter the FortiSASE domain name in the FortiExtender GUI as a static discovery server:
* Manually configuring the FortiSASE domain name in the FortiExtender GUI allows the extender to discover and connect to the FortiSASE infrastructure.
* This static discovery method ensures that FortiExtender can establish a connection with FortiSASE using the provided domain name.
References:
* FortiOS 7.2 Administration Guide: Details on FortiExtender deployment methods and configurations.
* FortiSASE 23.2 Documentation: Explains how to connect and configure FortiExtender with FortiSASE using FortiZTP and static discovery.
NEW QUESTION # 17
Refer to the exhibit.
In the user connection monitor, the FortiSASE administrator notices the user name is showing random characters. Which configuration change must the administrator make to get proper user information?
- A. Configure the username using FortiSASE naming convention.
- B. Add more endpoint licenses on FortiSASE.
- C. Turn off log anonymization on FortiSASE.
- D. Change the deployment type from SWG to VPN.
Answer: C
Explanation:
In the user connection monitor, the random characters shown for the username indicate that log anonymization is enabled. Log anonymization is a feature that hides the actual user information in the logs for privacy and security reasons. To display proper user information, you need to disable log anonymization.
* Log Anonymization:
* When log anonymization is turned on, the actual usernames are replaced with random characters to protect user privacy.
* This feature can be beneficial in certain environments but can cause issues when detailed user monitoring is required.
* Disabling Log Anonymization:
* Navigate to the FortiSASE settings.
* Locate the log settings section.
* Disable the log anonymization feature to ensure that actual usernames are displayed in the logs and user connection monitors.
References:
* FortiSASE 23.2 Documentation: Provides detailed steps on enabling and disabling log anonymization.
* Fortinet Knowledge Base: Explains the impact of log anonymization on user monitoring and logging.
NEW QUESTION # 18
How does FortiSASE hide user information when viewing and analyzing logs?
- A. By encrypting data using advanced encryption standard (AES)
- B. By hashing data using Blowfish
- C. By hashing data using salt
- D. By encrypting data using Secure Hash Algorithm 256-bit (SHA-256)
Answer: C
Explanation:
FortiSASE hides user information when viewing and analyzing logs by hashing data using salt. This approach ensures that sensitive user information is obfuscated, enhancing privacy and security.
* Hashing Data with Salt:
* Hashing data involves converting it into a fixed-size string of characters, which is typically a hash value.
* Salting adds random data to the input of the hash function, ensuring that even identical inputs produce different hash values.
* This method provides enhanced security by making it more difficult to reverse-engineer the original data from the hash value.
* Security and Privacy:
* Using salted hashes ensures that user information remains secure and private when stored or analyzed in logs.
* This technique is widely used in security systems to protect sensitive data from unauthorized access.
References:
* FortiOS 7.2 Administration Guide: Provides information on log management and data protection techniques.
* FortiSASE 23.2 Documentation: Details on how FortiSASE implements data hashing and salting to secure user information in logs.
NEW QUESTION # 19
What are two advantages of using zero-trust tags? (Choose two.)
- A. Zero-trust tags can be used to create multiple endpoint profiles which can be applied to different endpoints
- B. Zero-trust tags can be used to allow or deny access to network resources
- C. Zero-trust tags can determine the security posture of an endpoint.
- D. Zero-trust tags can be used to allow secure web gateway (SWG) access
Answer: B,C
Explanation:
Zero-trust tags are critical in implementing zero-trust network access (ZTNA) policies. Here are the two key advantages of using zero-trust tags:
* Access Control (Allow or Deny):
* Zero-trust tags can be used to define policies that either allow or deny access to specific network resources based on the tag associated with the user or device.
* This granular control ensures that only authorized users or devices with the appropriate tags can access sensitive resources, thereby enhancing security.
* Determining Security Posture:
* Zero-trust tags can be utilized to assess and determine the security posture of an endpoint.
* Based on the assigned tags, FortiSASE can evaluate the device's compliance with security policies, such as antivirus status, patch levels, and configuration settings.
* Devices that do not meet the required security posture can be restricted from accessing the network or given limited access.
References:
* FortiOS 7.2 Administration Guide: Provides detailed information on configuring and using zero-trust tags for access control and security posture assessment.
* FortiSASE 23.2 Documentation: Explains how zero-trust tags are implemented and used within the FortiSASE environment for enhancing security and compliance.
NEW QUESTION # 20
Which role does FortiSASE play in supporting zero trust network access (ZTNA) principles9
- A. It integrateswith software-defined network (SDN) solutions.
- B. It offers hardware-based firewalls for network segmentation.
- C. It enables VPN connections for remote employees.
- D. It can identify attributes on the endpoint for security posture check.
Answer: D
Explanation:
FortiSASE supports zero trust network access (ZTNA) principles by identifying attributes on the endpoint for security posture checks. ZTNA principles require continuous verification of user and device credentials, as well as their security posture, before granting access to network resources.
* Security Posture Check:
* FortiSASE can evaluate the security posture of endpoints by checking for compliance with security policies, such as antivirus status, patch levels, and configuration settings.
* This ensures that only compliant and secure devices are granted access to the network.
* Zero Trust Network Access (ZTNA):
* ZTNA is based on the principle of "never trust, always verify," which requires continuous assessment of user and device trustworthiness.
* FortiSASE plays a crucial role in implementing ZTNA by performing these security posture checks and enforcing access control policies.
References:
* FortiOS 7.2 Administration Guide: Provides information on ZTNA and endpoint security posture checks.
* FortiSASE 23.2 Documentation: Details on how FortiSASE implements ZTNA principles.
NEW QUESTION # 21
Refer to the exhibits.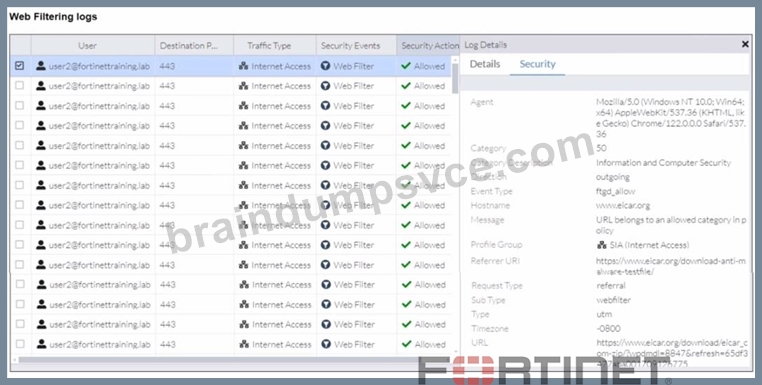


A FortiSASE administrator has configured an antivirus profile in the security profile group and applied it to the internet access policy. Remote users are still able to download the eicar.com-zip file from https://eicar.org.
Traffic logs show traffic is allowed by the policy.
Which configuration on FortiSASE is allowing users to perform the download?
- A. IPS is disabled in the security profile group.
- B. Force certificate inspection is enabled in the policy.
- C. Web filter is allowing the traffic.
- D. The HTTPS protocol is not enabled in the antivirus profile.
Answer: C
Explanation:
Based on the provided exhibits and the configuration details, the reason why users are still able to download the eicar.com-zip file despite having an antivirus profile applied is due to the Web Filter allowing the traffic.
Here is the step-by-step detailed explanation:
* Web Filtering Logs Analysis:
* The logs show that the traffic to the destination port 443 (which is HTTPS) is allowed and the security event triggered is Web Filter.
* The log details indicate that the URL belongs to an allowed category in the policy and thus, the traffic is permitted by the Web Filter.
* Security Profile Group Configuration:
* The Web Filter with Inline-CASB section indicates that the sitewww.eicar.orgis being monitored (93 occurrences) and not blocked.
* Since the Web Filter is set to allow traffic from this site, the antivirus profile will not block it because the Web Filter decision takes precedence.
* Antivirus Profile Configuration:
* Although the antivirus profile is configured, the logs do not show any antivirus actions being triggered. This indicates that the web filter is overriding the antivirus action.
* Policy Configuration:
* The policy named "Web Traffic" shows that it has logging enabled and is set to accept traffic.
* The profile group "SIA" applied to this policy includes both Web Filter and Antivirus settings.
However, since the Web Filter is allowing the traffic, the antivirus profile does not get the chance to inspect it.
References:
* FortiGate Security 7.2 Study Guide: Provides details on the precedence of web filtering over antivirus in security profiles.
* Fortinet Knowledge Base: Detailed explanation of web filtering and antivirus profiles interaction.
NEW QUESTION # 22
During FortiSASE provisioning, how many security points of presence (POPs) need to be configured by the FortiSASE administrator?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: A
Explanation:
During FortiSASE provisioning, the FortiSASE administrator needs to configure at least one security point of presence (PoP). A single PoP is sufficient to get started with FortiSASE, providing the necessary security services and connectivity for users.
* Security Point of Presence (PoP):
* A PoP is a strategically located data center that provides security services such as secure web gateway, firewall, and VPN termination.
* Configuring at least one PoP ensures that users can connect to FortiSASE and benefit from its security features.
* Scalability:
* While only one PoP is required to start, additional PoPs can be added as needed to enhance redundancy, load balancing, and performance.
References:
* FortiOS 7.2 Administration Guide: Provides details on the provisioning process for FortiSASE.
* FortiSASE 23.2 Documentation: Explains the configuration and role of security PoPs in the FortiSASE architecture.
NEW QUESTION # 23
You are designing a new network for Company X and one of the new cybersecurity policy requirements is that all remote user endpoints must always be connected and protected Which FortiSASE componentfacilitates this always-on security measure?
- A. site-based deployment
- B. thin-branch SASE extension
- C. inline-CASB
- D. unified FortiClient
Answer: D
Explanation:
The unified FortiClient component of FortiSASE facilitates the always-on security measure required for ensuring that all remote user endpoints are always connected and protected.
* Unified FortiClient:
* FortiClient is a comprehensive endpoint security solution that integrates with FortiSASE to provide continuous protection for remote user endpoints.
* It ensures that endpoints are always connected to the FortiSASE infrastructure, even when users are off the corporate network.
* Always-On Security:
* The unified FortiClient maintains a persistent connection to FortiSASE, enforcing security policies and protecting endpoints against threats at all times.
* This ensures compliance with the cybersecurity policy requiring constant connectivity and protection for remote users.
References:
* FortiOS 7.2 Administration Guide: Provides information on configuring and managing FortiClient for endpoint security.
* FortiSASE 23.2 Documentation: Explains how FortiClient integrates with FortiSASE to deliver always-on security for remote endpoints.
NEW QUESTION # 24
To complete their day-to-day operations, remote users require access to a TCP-based application that is hosted on a private web server. Which FortiSASE deployment use case provides the most efficient and secure method for meeting the remote users' requirements?
- A. next generation firewall (NGFW)
- B. zero trust network access (ZTNA) private access
- C. inline-CASB
- D. SD-WAN private access
Answer: B
Explanation:
Zero Trust Network Access (ZTNA) private access provides the most efficient and secure method for remote users to access a TCP-based application hosted on a private web server. ZTNA ensures that only authenticated and authorized users can access specific applications based on predefined policies, enhancing security and access control.
* Zero Trust Network Access (ZTNA):
* ZTNA operates on the principle of "never trust, always verify," continuously verifying user identity and device security posture before granting access.
* It provides secure and granular access to specific applications, ensuring that remote users can securely access the TCP-based application hosted on the private web server.
* Secure and Efficient Access:
* ZTNA private access allows remote users to connect directly to the application without needing a full VPN tunnel, reducing latency and improving performance.
* It ensures that only authorized users can access the application, providing robust security controls.
References:
* FortiOS 7.2 Administration Guide: Provides detailed information on ZTNA and its deployment use cases.
* FortiSASE 23.2 Documentation: Explains how ZTNA can be used to provide secure access to private applications for remote users.
NEW QUESTION # 25
Refer to the exhibit.
To allow access, which web tiller configuration must you change on FortiSASE?
- A. URL Filter
- B. inline cloud access security broker (CASB) headers
- C. content filter
- D. FortiGuard category-based filter
Answer: A
Explanation:
The exhibit indicates that the URLhttps://www.bbc.com/is being blocked due to containing a banned word ("fight"). To allow access to this specific URL, you need to adjust the URL filter settings on FortiSASE.
* URL Filtering:
* URL filtering allows administrators to define policies that block or allow access to specific URLs or URL patterns.
* In this case, the URL filter is set to block any URL containing the word "fight."
* Modifying URL Filter:
* Navigate to the Web Filter configuration in FortiSASE.
* Locate the URL filter settings.
* Add an exception for the URLhttps://www.bbc.com/to allow access, even if it contains a banned word.
* Alternatively, remove or adjust the banned word list to exclude the word "fight" if it's not critical to the security policy.
References:
* FortiOS 7.2 Administration Guide: Provides details on configuring and managing URL filters.
* FortiSASE 23.2 Documentation: Explains how to set up and modify web filtering policies, including URL filters.
NEW QUESTION # 26
......
Get Ready to Pass the FCSS_SASE_AD-23 exam Right Now Using Our Fortinet Certified Solution Specialist Exam Package: https://www.braindumpsvce.com/FCSS_SASE_AD-23_exam-dumps-torrent.html
Enhance Your Career With Available Preparation Guide for FCSS_SASE_AD-23 Exam: https://drive.google.com/open?id=1JbexwagPm1JVX1BIb-Q9MUcxJ1XAuu8p